OK – your WordPress site is hacked. Now what? Questions we frequently get from new users are, “Why was my WordPress site hacked?” and “What should I do after a WordPress hack?”
Of course, these are reasonable questions to ask; it’s extremely frustrating to find out that your site has been compromised and you need to tackle a malware infection or increase security controls. Surely you’d want to understand why and how to quickly deal with your hacked WordPress site.
However — while all websites are susceptible to hacks, certain errors could be increasing the vulnerability of your website. In this post, we’ll delve into a few of the main reasons why WordPress gets hacked and how it happens. We’ll also cover some common red flags and signs of a hacked WordPress environment, and what to do if your WordPress was hacked. This will help you to recognize potential mistakes, effectively recover from a hack, and take measures to safeguard your site from future attackers.
Contents:
- Why does WordPress get hacked?
- Key reasons why WordPress gets hacked
- What are the signs of a hacked WordPress site?
- What is the best way to prevent a WordPress hack?
- Getting help with hacked WordPress sites
Why does WordPress get hacked?
WordPress powers over 43% of all websites on the web, translating into hundreds of millions of websites worldwide. This popularity makes it a prime target for hackers, particularly websites that are not well-secured or contain known software vulnerabilities.
That being said, we need to make an important distinction: WordPress is not the only CMS platform targeted by hackers. In fact, to varying degrees all websites on the internet are prone to hacking attempts.
Understanding the hacker’s motive
Hackers have a wide range of motivations for their illicit activities. Some are merely novices learning to exploit less secure sites. Others might have more nefarious intentions, such as distributing malware, launching attacks on other websites, sending spam, or using compromised domains for black hat SEO.
Some attackers focus on stealing sensitive data such as personal information, credit card numbers, or login credentials. These can be sold on the dark web or used to commit fraud and identity theft. Others may simply be looking to disrupt services or make a political statement.
However, it’s important to note that not all hackers are motivated by illicit gains or malicious intent. Some hackers, often referred to as “white hat” hackers, exploit vulnerabilities in order to expose them and help improve the system’s security.
Regardless of the motive, the outcome of a hack is almost always detrimental to the website owner. It can lead to lost data, reputation issues, and even legal consequences if sensitive customer information is compromised.
Key reasons why WordPress gets hacked
Now that we understand the motivations behind a hack, let’s take a look at some of the key reasons why WordPress gets hacked.
- Unpatched WordPress core, plugins & themes
- Weak passwords and usernames
- Unprotected WordPress admin panels
- Improper isolation in shared server environments
- Unrestricted access to wp-config
Let’s go over these reasons in closer detail.
1. Unpatched WordPress core, plugins & themes
The core WordPress CMS is secure, but only if you maintain it to the latest version and properly configure it.
Since the code base is publicly accessible, anyone can review and analyze the source code. And whenever a bug or security issue is reported by the open-source community, developers update WordPress core to patch the issue.
However, these updates don’t apply to your extensible components like plugins and themes. You’ll need to patch each piece of software individually (and on a regular basis) to mitigate risk.
Not updating your WordPress software and components can leave your site exposed to known issues. To protect your environment and mitigate risk, it’s crucial to update your WordPress core (along with all your plugins and themes) as soon as a new patch is available.
Hackers often use automated tools to quickly find and attack websites with known vulnerabilities — so it’s important to act quickly when it comes to software updates.
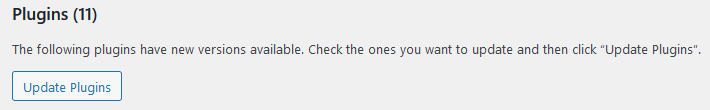
If you don’t have automatic plugin and theme updates enabled, you can manually update plugins in your WordPress dashboard from the following location: Dashboard > Updates > Plugins
2. Weak passwords and usernames
Passwords are your WordPress site’s first line of defense. Automated tools can easily crack a weak password, giving an attacker unauthorized access to your posts, pages, files and database.
That’s why it’s so essential to use strong, unique passwords for all your accounts, including:
- WordPress admin account
- Web hosting control panel account
- FTP accounts
- MySQL databases
- Email accounts used for WordPress admin and hosting
We recommend creating unique passwords with a combination of letters, numbers, and special characters — at least 12 characters long. Password generators can make it easy to quickly create new unique credentials for your accounts.
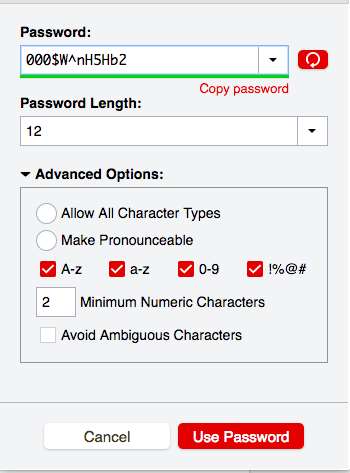
Furthermore, steer clear of default admin usernames; it only takes a second to change admin to something unique and makes it that much harder to guess the credentials to your account.
3. Unprotected WordPress admin panels
The WordPress admin area and default login pages /wp-login.php and /wp-admin are one of the most frequently targeted areas of WordPress. Since it’s where you can control all aspects of your website, it’s also consequently where hackers can do the most damage.
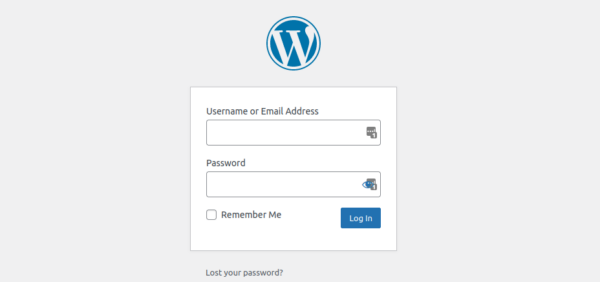
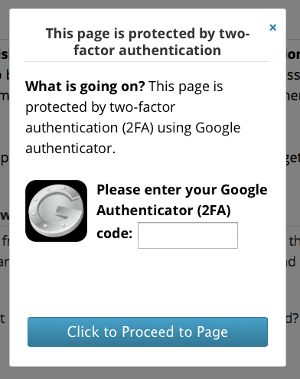
By default, WordPress does not limit the number of failed login attempts (nor does it contain any native 2FA system), rendering it particularly vulnerable to brute force attacks.
Protect your WordPress site by adding layers of authentication and restricting unauthorized access to sensitive pages like wp-login and wp-admin.
The Sucuri firewall makes it easy to implement protected pages across your website and provides options for password protection, 2FA, captcha and IP address restrictions.
Reach out to our experienced 24/7 team to get help with setup if you need a hand!
4. Improper isolation in shared server environments
We deal with plenty of new clients who have “soup kitchen servers”. These are web servers with a huge number of websites, installations, and configurations all crammed into the same environment.
The issue with these environments is that a single compromised website can infect all others on the shared account or server, leading to cross-site contamination.
You can help prevent this issue by using separate cPanel instances for each website and configuring a secure VPS environment with PHP-FPM to host multiple sites.
5. Unrestricted access to wp-config
The wp-config.php file is an integral part of your WordPress website. This core file is responsible for running your site and houses important configurations such as database location details, login credentials, and advanced options for database elements, security keys, and developers.
If you’re new to WordPress, it’s crucial to start by restricting access to this file. One way to do this is by moving your wp-config file one directory level above the root folder, making it inaccessible to the internet. If the file is not found in the root folder, WordPress will automatically search for it in the directory above the root.
For those whose servers use .htaccess: you can further restrict access by adding a rule to deny anyone searching for it.
The directives for Apache 2.4 are as follows:
<FilesMatch "wp-config\.php">
Require all denied
</FilesMatch">Salts and keys
The wp-config file includes a section dedicated to salts and keys that boost the security of cookies and passwords in transit between your browser and web server.
You can set up your salts and keys by adding or editing these lines after the other define statements:
define(‘AUTH_KEY’, ‘include salt here’);
define(‘SECURE_AUTH_KEY’, ‘include salt here’);
define(‘LOGGED_IN_KEY’, ‘include salt here’);
define(‘NONCE_KEY’, ‘include salt here’);Set file permissions
Since the wp-config.php file contains highly sensitive information, it’s essential to configure file permissions to prevent unauthorized access or modification.
A permission level of 600 should suffice, but you can start with 400 and escalate as necessary. Always begin with the least permissive configuration and only increase permissions when required. Never set permissions to 777 unless you’re an expert or have an excellent reason.
Disable plugin and theme installers
Wp-config can also define vital information about WordPress plugins and themes. For instance, you can disable the theme and plugin file editors or installers by adding the following lines to your wp-config file:
define( 'DISALLOW_FILE_EDIT', true ); //disables file editor define( 'DISALLOW_FILE_MODS', true ); //disables both file editor and installer
Bear in mind that this will also block plugin updates. You can still update plugins and themes using WP-CLI or manually via sFTP.
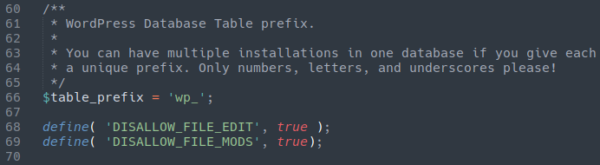
Attackers often exploit theme and plugin installers to install backdoors. So, this simple step can make it more challenging for them to create fake plugins for unauthorized access.
What are the signs of a hacked WordPress site?
Think your WordPress site is behaving strangely but not too sure if it was hacked? Let’s take a look at some of the most common red flags and warning signs of a hacked WordPress website:
- Can’t log in to the WordPress dashboard.
- There’s new content or static pages on your site.
- Browser warnings appear when you navigate to your site.
- Visitors are unexpectedly redirected to other websites.
- Google search results show warnings for your WordPress site.
- The hosting provider for your WordPress site is warning about unusual activity.
- A security plugin is warning you about unexpected changes, logins, new users, or malware detections.
Can’t log in to the WordPress dashboard.
Can’t log in to your WordPress dashboard? Well, there’s no point in assuming you’ve been hacked just yet. Before you start panicking, try a simple password reset to rule out the fact that you might have just forgotten your password.
If a password reset doesn’t work or you don’t receive the reset email, then this is a red flag that something unusual may have occurred and warrants further investigation.
Our security analysts often find that attackers delete the WordPress admin user or change user passwords to prevent access once they hack the site. So, if you are unable to reset your password and you believe that your account was deleted or tampered with, this is a definite sign of a hacked WordPress site.
There’s new content or static pages on your site.
In some cases hackers will compromise a website to deface it or inject it with SEO spam content. But, it makes sense to check with other website editors and admins before you outright assume it’s a hack.
If you find new, unexpected content or pages on your website and you’re certain that you (or another legitimate website user) didn’t put it there, your site was likely compromised and you’ll need to do a bit more digging.
New content doesn’t just mean full paragraphs of text, either — sometimes attackers will try to hide spam text in hidden divs or inject links to spammy websites into your existing website pages. In other cases, they will generate entirely brand new pages on your website.
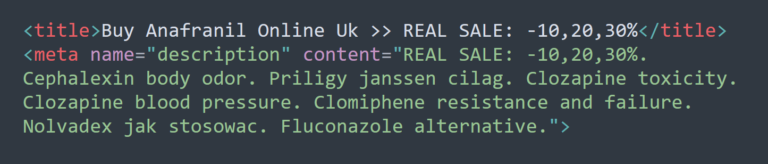
So, if you just encountered some strange spammy keywords, content, links or other signs of website tampering, you’ll want to scan and check your site for malware.
Browser warnings appear when you navigate to your site.
To protect users, modern web browsers use automated processes to detect website malware. Data from a wide range of sources is collected and aggregated to help find websites that might be harmful to website visitors.
So if a browser like Chrome, Firefox, or Edge detects malware on your website, they’ll issue a warning to help prevent visitors from navigating to the website until the problem is fixed. This is most certainly a sign of a hack and should be investigated further.
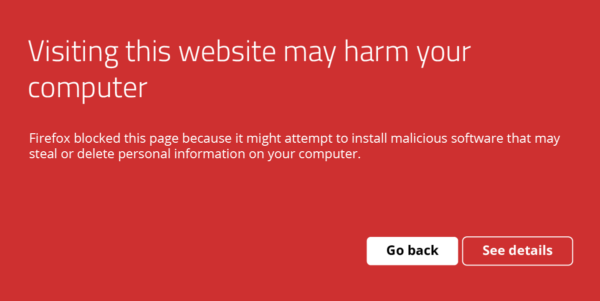
In most cases, the browser warning will likely contain information on how to diagnose or resolve the problem. But you will certainly want to take steps to find and fix the hack on your WordPress site.
Visitors are unexpectedly redirected to other websites.
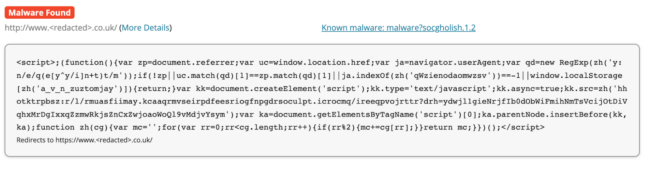
Hackers are known to add redirect scripts to compromised websites in order to monetize traffic to third-party spam sites, trick victims into loading and installing fake browser updates, or even distribute malware.
Scripts that execute malicious redirects can lurk anywhere on a website. We’ve seen them in databases where they differentiate between real traffic and search engine bots, and then sent legitimate traffic to a malware download.
The malicious redirect was triggered from a search engine results page, not within the infected website. One click, and wham — malware starts downloading.
So, if your website is redirecting you or website visitors to strange and unexpected websites, this is definitely a sign of a hack. You’ll want to scan for injected malware as soon as possible.
Google search results show warnings for your WordPress site.
Just like web browsers, search engines like Google also have a vested interest in protecting users. So if Google’s algorithms and crawlers detect that there’s malicious code on your WordPress site, they will issue a “This site may be hacked” warning like this:
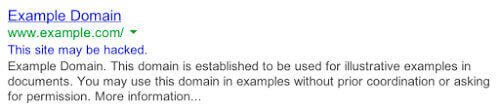
Google is pretty accurate when it comes to detecting website malware infections. If you see this warning for your site in search results, it’s a credible sign that your WordPress site was hacked.
The hosting provider for your WordPress site is warning about unusual activity.
Your hosting provider will reach out if they detect any wide range of problems, including but not limited to:
- Malware infection
- Server resource overuse
- Payment failures
- Terms of service violations
- Other important account activity
If your host has detected some unsual activity or a malware infection, you’ll want to take it very seriously and address it as soon as possible as it’s a definitely sign of an issue. If you don’t take measures to resolve the problem, you could risk an account suspension.
A security plugin is warning you about unexpected changes, logins, new users, or malware detections.
Security plugins like the Sucuri WordPress Plugin contain a wide range of useful security features that can help you detect malicious behavior on your WordPress site.
If the plugin finds website malware or detects unexpected changes to your files, you’ll be able to know pretty quickly to determine if your site is hacked or not.
What is the best way to prevent a WordPress hack?
The unfortunate reality is that no single security measure can provide a 100% guarantee against hackers. However, implementing a defense-in-depth strategy that includes hardening your WordPress website and leveraging a reliable website firewall can significantly improve your chances of preventing a hack.
The Sucuri firewall helps to ward off brute force attacks, blocking any unwarranted access to your wp-admin or wp-login page and preventing automated attacks. It also mitigates Distributed Denial of Service (DDoS) attacks, which try to overwhelm a server or application resources. Another excellent feature is its ability to virtually patch known vulnerabilities in the event that you’re unable to update your website software in a timely manner.
There’s no installation necessary — just a simple switch of your DNS A Record to enable it. For further details, check out this video on how to prevent a hack with a website firewall.
Getting help with hacked WordPress sites
Pretty certain that your WordPress site was hacked? We’ve got your back!
If you’re the do-it-yourself type, we’ve got a comprehensive guide that details all the steps you can take to respond to a hacked site and clean up WordPress malware.
Some key steps to respond to a hacked WordPress site include:
- Scan your WordPress site for malware and signs of infection
- Check core WordPress file integrity
- Remove malware from your WordPress files and database
- Get rid of website backdoors to prevent reinfection
- Secure WordPress user accounts
- Patch and update your website software, plugins, and themes
- Harden your WordPress environment
You’ll find all these and more in the how to fix a hacked WordPress guide. Just follow along and reach out if you get stuck!
For those that need a hand or want some help as soon as possible, our experienced security analysts are available 24/7 around the clock to help you remove malware from WordPress and get your site protected from future hacks. Sign up for the plan that best suits your needs or chat with us to learn more!



![Malware comes in many different varieties. Analyst Krasimir Konov is on this month’s Sucuri Sit-Down to help keep them all straight. From malicious iframes to SEO spam, join host Justin Channell as he racks Krasimir’s brain on all the different types of malware. Also, Krasimir discusses his recent blog post about a malicious cURL downloader, and Justin breaks down the latest website security news, including patched plugins you should update. Podcast Transcript Justin Channell: Hello, and welcome to the Sucuri Sit Down. I'm your host, Justin Channell, and this is a monthly podcast about website security, where we get in-depth with the malware removal experts here at Sucuri. Later in the show, I'll have our analyst Krasimir Konov to chat about some different types of malware, but first, let's take a look at other topics we've published on our blog and Sucuri labs notes this month. First up, we have some new information about credit card skimming with hackers using a hybrid method to steal payment information from eCommerce websites. Our analyst Dennis Sinegubko wrote about this for the Sucuri blog back at the beginning of June. Now, most credit card stealing malware is a client side JavaScript that grabs data and sends it to a third party server. But, that approach has a drawback for bad actors because it's still possible to track the requests and catch them as being suspicious. Now, to get around that, bad actors have started harvesting information server side by modifying core PHP files. In this case, the infection would be undetectable from the outside, but it's still going to be pretty easy to find because you're rarely modifying any of those core files, so any of those changes that are going to come up are going to be suspicious. To get around both of these drawbacks, we're seeing bad actors combine the two. So client side snippets of JavaScript are sending stolen credit card data to server side scripts that they've installed on the same server as the site. Now, this allows bad actors to cover their tracks a little bit because the traffic that's being redirected is going to the same server, and that's less likely to be flagged as suspicious. It's a bit more complicated to pull this off, but our team has been seeing this hybrid approach in the wild, so it's something to be on the lookout for. Now, another month has passed, and we found more cross site scripting attacks targeting WordPress plugins. Most notably, we discovered one that affects users of the YITH WooCommerce Ajax Product Filter plugin. Now, this is a plugin that allows WooCommerce stores to be filtered by product type, and it's pretty popular. It's got about 100,000 users right now, so with it being vulnerable, it's very important that all of them update to the latest version, which is 3.11.1. Some of the other plugins we found cross site scripting vulnerabilities with included Elementor Page Builder, Careerfy, JobSearch, and Newspaper. If you're looking for a full list of vulnerabilities that have been patched this month, John Castro at the Sucuri Labs blog has you covered. Check out our show notes for the link. Also, this month I had a blog go up detailing what's called a jibberish hack. It's basically the same motivation as an SEO spam attack where bad actors use your site's good standing to redirect visitors to their own sites. But in this attack, you'll find a bunch of randomly named folders filled with a ton of HTML files with really nonsensical file names like cheap-cool-hairstyles-photos.html. It's just going to be a mishmash of keywords that clearly you didn't put there. Unfortunately, just deleting all those HTML files and folders is not going to be enough to get rid of that jibberish hack though. You're going to need to fully clean any hacked files and database tables, and then you're going to have to deal with all the damage caused to your site's standing. And just keep in mind, if you find anything about that process too daunting, we're always here to help. Now, for this month's Sit Down, we have Sucuri analyst Krasimir Konov. Earlier in June, he had written a lab's note about a malicious downloader script that used the curl function, and we chatted a bit about it, but more importantly, we went really in-depth on all the different varieties of malware that website owners need to be aware of. But, before I get started with Krasimir, I just wanted to remind you about the Sucuri Sync-Up, our sister podcast. It's a weekly website security news briefing that you can find anywhere you get your podcasts, as well as the video version on our social media feed, and now you can even get it on your Amazon Alexa smart speakers. Just search Amazon skills for Sucuri Sync-Up, add the flash briefing, and get new content delivered every Monday. Now, on with the show. Hi Krasimir, thanks for joining us on the show. I thought we could start off and maybe have you tell us a little bit about yourself and what you do here at Sucuri? Krasimir Konov: Yeah, sure. Well, I joined Sucuri originally in 2014, but I've been in the IT business for about 10 years. Nine of those I did security. And currently at Sucuri I'm one of the malware analysts. I used to work in the front lines, used to clean websites and whatnot, and then I gradually moved up, and now I'm working in the malware research department. And my day to day job is basically analyzing malware, and then once I analyze it and figure out what it is, then I will create a signature for it. And we'll add those signatures to our tools, so we can automate some of the work we do. And I also write some Labs Notes blog posts. Usually, if I find something interesting in malware or some security topic, I'll write about it. Justin Channell: Yeah. And of those topics recently that you wrote about, one was about a malicious curl downloader, and how exactly did that work? Krasimir Konov: Right, yeah. That was an interesting one, but not very unique or anything like that. We see that a lot with curl being used as a downloader. It's a very common malware. So rather than including the actual malware in the file, the attackers would use curl to download the malicious code. In this case, they'll download it from Pastebin, but it could be anything. It could be another website or anything like that, and curl would just make a call to the website, request the code. The website will respond with the code, and then later on, there is some code to either save the output somewhere on the website, or you'll just run it through eval and execute the actual code right away. Justin Channell: Right. And you said that it's commonly found in malware, but let's kind of maybe talk a bit broader about malware in general. What is everything that is classified as malware? Krasimir Konov: Well, in general it will be anything that the owner of the website didn't authorize, anything that was added by a third party. There is a lot of different malware. It could be even something like a defacement that will also be considered malware because it was something the user did not authorize. Even though it might not be doing anything malicious on the website, it's not infecting users, the visit is still something they did not authorize. So defacement would also be considered malware. And even something like ransomware where the website is technically not really damaged, it's all encrypted, but it's not infecting anybody. It's not doing anything malicious, but it's still encrypting the entire website and asking the user or the customer, the owner of the website for a ransom they need to pay in order to get the website back online. Justin Channell: Okay. Let's maybe break it down to each individual type of malware. For example, what would be a way that maybe I-frames could be maliciously used by a hacker? Krasimir Konov: Yeah. An I-frame can be used maliciously when it loads content from another location. You can look at the I-frame as a window that just opens another website. So anything that website has on it, you're pretty much loading it through the I-frame. So if that website is infected and it's serving some kind of malware, by opening an I-frame, you're loading all those elements, everything that was on this website. And sometimes the I-frame can be as small as pixel or something hidden somewhere off the screen, so you wouldn't even know that it was opening it. Justin Channell: And yeah, I feel like we've also seen a lot of them where they're used almost to mimic popups as well. Krasimir Konov: Yeah. I mean the I-frame, it could just load from another website and the other website could do anything. It could be serving just malware and it would try to infect the user that doesn't even know that they're being connected to the other website. It could just have some other JavaScript that's just trying to open up pop ups on the original website through the I-frame. Yeah, it could be a lot of things. Justin Channell: Okay. And also, let's talk a little bit about conditional redirects and how those work. What allows a script to detect which devices are coming in and where they're coming from? Krasimir Konov: Right. Yeah. That's a common one we see a lot. Basically, a conditional redirect would be something, it's a redirect on the website. It's obviously malicious, but there's certain conditions that need to be met before the redirect is actually executed or the redirect happens. For example, let's say if it's on a phishing website or a phishing page that is hidden somewhere on the website. For example, if Google visits it, obviously the attacker doesn't want Google to see the actual phishing page and record it as a phishing page. So they'll look for, for example, the IP address. They would look for the user agent. And a lot of times they can tell that it's a bot. So they'll just return a 404 response, for example, that will be like, "Oh, page not found." So Google would be like, "Oh, it looks like this page doesn't exist." But then if a regular user goes to the same page, then those conditions will be met. The actual website or the script behind the phishing will check and see, and be like, "Oh, this one is running Firefox or Chrome," and be like, okay. And then they'll look at the IP and be like, "Oh, he's in whatever, he's in United States somewhere." And he's like, "Oh, okay. That's good." And then once all of these conditions are met, then the actual script will serve them the actual phishing page. And it'll be like, "Oh, you need to fill out this to recover your account or whatever, or type in your credentials to log in here." Justin Channell: And so this is the type of thing we're really, a website owner is going to run into this more commonly when people are complaining about they're getting served bad content or whatever, and they can't seem to replicate it. It's likely probably these kind of redirects. Is that right? Krasimir Konov: Right, right. It could be something as specific as, for example, a range of IP addresses that correspond to an ISP or maybe let's say a country. It could be like, "Oh, were targeting only customers in the US," so if you're connecting from another country and you go to the same website or the same page, it would just say 404. It will give you a page not found. But then if you actually have an IP address from the United States, you're connecting from the United States, then it will actually show you the phishing page. Justin Channell: Now another type of malware I feel like we see a lot here is SEO spam. We hear people talking about that. What are some of the top SEO spam keywords that you see coming through? Krasimir Konov: Yeah. We get that a lot. We see a lot of spam on websites. A lot of times attackers will use SEO spam to gain ranking for their own website. Or they'll just try to include some kind of SEO spam in links to another website that they're currently running or something. I mean, these things change all the time. So a website might be up for a week and then it'll disappear, and then they'll start another campaign. But yeah, we see that a lot. We see all kinds of keywords they use. Most common ones will be something like Viagra. We'll have like jerseys for sale. A lot of times, they'll use name brands like Nike, Rolex, Prada. We've seen even some essay writing services for some reason. I'm not sure why, but that's common. We see, for example, pharmaceuticals a lot that will use specific medicine names. They'll use all kinds of replicas, like a replica bag of this, replica this, replica that. We'd see prescription, also payday loans. And obviously there's some adult related sites and things like that keywords. Justin Channell: So pretty much anything that people are going to be searching and clicking on are probably going to be targets for SEO spam? Krasimir Konov: Right. I think a lot of it commonly is pharma related because a lot of people are looking to buy medicine online, and a lot of times will require a prescription. So a lot of people are like, "Oh, let me see if I can find this medicine that I can buy it online somewhere." They don't need a prescription. They don't want to pay to visit a doctor and whatnot, and they'll look for it. And yeah. Justin Channell: Now, whenever somebody's website does get hacked with a SEO spam attack, what kind of effect can it have on the website beyond just being defaced? Krasimir Konov: Yeah. You can have a lot of things can happen, negative things. For example, the website can be blacklisted because of the keywords. And that usually represents a big red warning when you go on the website, depending on who blacklisted it. But if it's Google, for example, you'll see a big warning and it'll tell you this website contains malware or there's something wrong with this website. So, pretty much all the traffic on the website will be gone. And then you can also lose a lot of your reputation if there is a SEO spam on the website. For example, if you were ranked in say number five for certain keywords that represent your product on Google search engines, and then suddenly you get hit with SEO spam, then all these search engines then go and visit the website. And all of a sudden they're like, "Oh, there's all these weird key words on here, all this SEO spam that's causing a lot of mixed signals." And the search engines are like, "Oh, where do we rank this website now? Do we rank them with this product that's originally what the website is about? Or do we take into consideration all these other keywords that are mixed up that are SEO spam?" So, all of a sudden your website might go from being ranked number five on the first page to being on the 10th page. And then you rank for all these other keywords that you didn't intend to. And then people search for something completely different. They're searching for jerseys or something, or now they're searching for Prada products, and then suddenly your website pops up in there. So you're not really getting any good traffic, not targeted traffic. But, yeah. Justin Channell: Okay. So in a lot of ways, the effects of SEO spam would kind of be the same for defacements or any kind of malware with the blacklisting, but it does bring that kind of unique part to it where then it can also then bring traffic that you weren't expecting from somebody searching for jerseys, for example. I had not really ever thought about that. Krasimir Konov: Right, right. Yeah. It will definitely bring some traffic. I've seen a lot of times where websites will be connected. Let's say, there was 1,000 websites that were all infected with SEO spam, and it will kind of link each other to try to bring each other up into the rankings. And so you would see a lot of strange traffic from some random websites that were, for example, that were previously infected, even if they might not be anymore. But yeah, they'll be sending traffic to you or there'll be usually search engines sending you traffic, but for the wrong keywords. People are looking for something else, so obviously they're not going to be interested in your website. They're not going to buy anything because they're not looking for that. Justin Channell: And now, so thinking of the way websites get infected, a very common way it seems to be is through phishing campaigns. What are some recommendations you have for the best ways to avoid becoming a phishing victim? Krasimir Konov: Yeah. There is some ways. I mean, it depends really on the type of attack. Obviously, a lot of people, when they think of phishing, they think, "Oh, it's just like a PayPal phishing page and it just looks like the original," but it could be more subtle. If it's just a regular page where you're just going and you get redirected to another website, obviously the first thing to look is if you have the security padlocks, make sure that traffic is encrypted. A lot of these websites don't really have any encryption nowadays. More are starting to get that with pre SSLs being issued and whatnot. But that's the first thing to look and see, make sure. Anywhere you're typing your sensitive information, you want to make sure you have the padlock to make sure everything is encrypted. Krasimir Konov: But also you want to look at the URL of the actual website you're visiting. A lot of times they'll try to hide it. So you might have to be careful and look closely. Something that might be an I will be an L or something like that. And a capital I and L might look kind of similar into your IRL, so you might miss something like that. Say, if you're looking for PayPal and it might replace the L with an I, and if you don't look closely, it might look exactly the same. And you're like, "Oh, okay, it's paypal.com," but not really. So yeah. Just pay attention to the URL, make sure it is the actual website. There's no paypal.com dot something, dot something else, dot com. Yeah. You want it to just say paypal.com, and then it'll have forward slash and something else. But yeah, it gets more complicated when you have, for example, a phishing page that's injected into a regular page. For example, you have a checkout page on a website that you're buying things from and you go through the checkout page and you're looking at where you type in your credit card information and whatnot. And you might have a phishing page that actually looks exactly like a little box that gives you where you put in your credit card number, or your name, your address, and all that. So that will be more subtle. For example, that could be also an I-frame that's just coming from another page. And it will look exactly like it's part of the website. You're on the legitimate website, but only that portion of the website is actually the phishing page. And you look at it and you're like, "Oh, okay. It looks fine. I'm just putting my credentials." So that one could be a lot harder to figure it out. Usually, if it's something like that, I look for something that looks kind of out of place. Maybe they didn't get the right font. It might not be the same as the original website or there might be something out of place, some fields that are missing or some fields that are squished into the left or the right. It looks kind of awkward. It's like, why would this be like this? The whole website looks professional. There's a pink background or something, for example, and then suddenly there's this white box in the middle. It's like, ah, it looks kind of weird, out of place. Justin Channell: So pretty much if anything looks slightly out of place, you really should double check everything at that point. Krasimir Konov: Right. Right. Yeah. Obviously there's more ways that you can check, but I wouldn't get into more technical, like inspecting elements and looking at stuff, but yeah. Justin Channell: And now another type of malware that's kind of, and it kind of plays in with whatever the other infection is, is backdoors. Can you give us some examples of what backdoors can be? It's mainly just when a hacker can get back into the site to reinfect it, but I know there are a ton of different methods. And what are some of the more common ones and then maybe some that really interesting that you've seen? Krasimir Konov: Yeah, there is a lot. They'll probably be one of the first things the hacker would do is if they compromise a website, obviously they'll try to spread backdoors and just inject code everywhere so they can get back in, even if the owner of the website or webmaster cleans it. They want to try and hide some malicious code somewhere so they can always get back in. There's many variations. A backdoor could be something as simple as a single line of code to just [inaudible 00:20:19] argument, some kind of string or something via get or post. Krasimir Konov: And then it runs into an eval, so it evaluates the code and executes it. And some backdoors are very complex and they can be included in, let's say you have a WordPress site and you have a specific login page where all the login credentials are being processed and everything else. They could even inject code into that to basically bypass the whole login mechanism so that they can just bypass everything. They don't even have to know any user. They don't have to know the password, nothing. They'll just include some lines in there, and every time they'll be just able to log in. Yeah. It gets pretty crazy. Yeah. I mean, there's all kinds of malware. There is always a malware, for example, that just targets credit cards and will just target the eCommerce websites. And they'll just try to steal the login credentials, I mean, the credit cards. They'll try to get your address, your credit card information, any kind of CVV code or whatever you typed into the billing address, everything. And then there's also malware like the backdoors that are just trying to keep the attacker in control and trying to get them back into the website. There's just so many variations of what a malicious user might want to do on a website. Some can be something as simple as just reinfecting the website. They don't want to keep control. They just want to keep reinfecting it with some kind of malware. So even if you clean it, it would just get reinfected. Some of them in the database, otherwise might be in the files. We've seen some added into a [inaudible 00:22:14] job that just keeps running on the server. There could be malware that is just a giant to, for example, attack out of websites. Like for example, a distributed denial service where they put the same malware on thousands of websites. And then they try to send traffic to one website to try to bring it down. Yeah. People try to do all kinds of stuff with websites. We've seen even some cryptocurrency mining malware that you go onto a website and suddenly your PC starts running like crazy. And you're like, what the hell is going on? Your fans turn on and the PC is 100% CPU. And it turns out that the website has some malware that's just by mining Bitcoins with your CPU and it's using all of it. Justin Channell: Wow. Okay. So one question now, the last question I have is of all the malware that you've seen, what do you think is the coolest piece of malware that you've ever seen? Krasimir Konov: I think the coolest would be the ones that are so subtle that you don't even know that it's there. For example, we've seen some that were pretty innovative. It will be just a one liner code that's just one line. And for example, it will be let's say 40-50 characters, something like that. And that's all it is. And they'll hide it somewhere in between the legitimate code. And if you don't know what you're looking for, you would never see it. It doesn't look suspicious. There is no links to some other website. There's no some kind of encrypted code or anything like that. It's just a simple one line. And then if you're just scrolling through the file looking for something, you would never see it. It just looks like all the other code. And then if you look closely, you're like, "Oh, there's this..." Look closely, and you're like, "Oh wow, this is not supposed to be there." And then you keep looking at it and you're like, "This looks really weird." And then you see that it's actually doing some malicious things and trying to evaluate some code or taking output from the outside, I mean, some input from outside, you can call it and give it code to run. Justin Channell: Well, Krasimir, thanks for coming on and talking to us for today. Krasimir Konov: Yeah. Thank you. Thank you. I'm so happy. I'm glad I was able to do this podcast and I can't wait to do another one. Justin Channell: Yeah, we'll have you on again. Thanks. Krasimir Konov: Thank you. Justin Channell: Thanks again to Krasimir for joining us here on the Sit Down. We'll be back with another episode next month. So be sure to subscribe on Apple podcasts, Spotify, Stitcher, or any podcasting platform. Also, be sure to follow us on social media at Sucuri Security and check us out at sucuri.net. That's S-U-C-U-R-I.net. I'm Justin Channell, And this has been the Sucuri Sit Down. Stay safe out there.](https://blog.sucuri.net/wp-content/uploads/2020/05/20-sucuri-podcast-blog-post_blog_image-390x183.jpg)